Vai al contenuto principale

#gao

Six Agencies Let DOGE Into the Building and Kept GAO on the Porch

Full and Prompt Access, Reserved for SomeThe executive order that created the Department of Government Efficiency told agency heads to give its person

Altro...

Full and Prompt Access, Reserved for SomeThe executive order that created the Department of Government Efficiency told agency heads to give its personnel full and prompt access to every unclassified record, software system, and IT system they owned. Agencies duly stood up DOGE teams and provisioned accounts. When the Government Accountability Office, which is Congress’s own auditor, asked six of them to demonstrate what that access looked like in practice, the enthusiasm curdled into a remarkable silence.

GAO’s new report, GAO-26-108192, covers the Consumer Financial Protection Bureau, the Departments of Education and Veterans Affairs, NOAA, the Securities and Exchange Commission, and the Small Business Administration. The audit ran from March 2025 to September 2026. After eighteen months, GAO’s conclusion is that it could not determine how far DOGE’s reach extended at any of them. Four agencies reported that DOGE teams touched more than 23 systems covering contracts, grants, human resources, and finances, but none supplied enough to verify the level of access. SBA and VA never even named the systems.

Let us be precise about what this is not. The report does not allege that anything was stolen, leaked, or misused. Its complaint is subtler and, for anyone who believes in oversight, arguably worse. It could not check.

A Catalogue of ExcusesThe reasons for not being checked are instructive, if only for their range.

VA and SBA went with the classic. GAO asked SBA repeatedly between May 2025 and February 2026, and as of this month the agency has not explained why it never answered. GAO asked VA repeatedly from April 2025 to May 2026, and in June the department confirmed it would neither address the requests nor say why. Nothing says accountability quite like a closed door with no sign on it.

NOAA and SEC preferred the constitutional approach. Their general counsels informed GAO that the auditors lacked authority to proceed, NOAA because the request came from a ranking member of a committee and SEC because it believed only a committee or its chair may ask. SEC added that certain information was protected from disclosure to GAO. Education cited ongoing litigation and worried about handing over personal information about DOGE staff without a guarantee of confidentiality. GAO, for the record, says it has routinely protected exactly this kind of information at the same level of confidentiality required of an agency head, and has obtained it from these very agencies before.

CFPB chose prose. Its lawyers called the inquiry a “fishing expedition,” described GAO’s requests as redundant, unnecessary, and disruptive to bureau operations, and accused the auditors of a fundamental misunderstanding of federal personnel management. In April, its chief legal officer wrote that GAO was serving at the behest of a few congressional members to harass the bureau. When GAO offered an exit conference to sort out the disagreements, CFPB declined. It did, however, ask GAO to reprint its April letter in the final report, which GAO did, along with the bureau’s September comments and annotated rebuttals in the margins. It is the closest thing to a duel the federal government has produced this year.

Notice the arithmetic here. An executive order demanded that DOGE receive full and prompt access. The same agencies then found the concept of prompt access to be considerably less appealing when the person asking carried a congressional badge instead of a White House one.

What the Cooperators GotThe most damning evidence that cooperation is possible comes from the agencies that offered it. In April 2026, GAO reported on the Treasury Department’s Bureau of the Fiscal Service and on the National Labor Relations Board. Both let auditors in. At the NLRB, GAO found no evidence that DOGE-affiliated staff accessed the human resources systems they had requested. At the Bureau of the Fiscal Service, it found the opposite kind of news, namely that the bureau had not fully implemented the security and privacy controls needed to protect sensitive payment data, and that one DOGE team member failed to secure information appropriately. GAO made six recommendations. As of September, none has been implemented.

So here is the pattern. Where auditors were admitted, the public got a clean answer in one case and an uncomfortable one in the other. Both are useful. That is what audits are for. Where auditors were turned away, the public got a shrug in a government letterhead.

The partial answers were not reassuring either. At CFPB, the bureau’s own policy requires data users to complete security and privacy training before touching data, and its guidance makes no exception for short-term detailees. GAO received documentation that all six DOGE team members got a privacy briefing but only four completed security training. Five of six signed the agreement not to knowingly create cybersecurity risks, and four of six reviewed the acceptable use policy. One CFPB team member had the ability to view, modify, and delete data in the bureau’s primary human resources system. At Education, signed IT rules of behavior for one of the six team members never materialized, despite repeated requests. At SEC, one background check was still underway and another dated from 2017, with no confirmation that it was favorably adjudicated.

CFPB and SEC each say they had no cybersecurity or privacy incidents involving their DOGE teams. Perhaps so. But neither would let GAO watch the systems that track incidents or log user activity, which makes the claim a promise rather than a finding. Government Auditing Standards, GAO patiently explains, call for corroborating testimony with something more reliable than the testimony.

Oversight by Permission SlipThe legal argument deserves attention because it would, if accepted, remake the balance of power between Congress and the executive branch. GAO points to 31 U.S.C. § 717(b)(1), which lets the Comptroller General conduct audits on his own initiative, and notes that Congress and multiple administrations have recognized work for ranking members over decades. Agencies that now insist only a committee chair may ask are not clarifying the law. They are discovering that a minority-party request is easy to ignore.

Most of the requesters here were ranking members, which is to say the minority. That is precisely who cannot compel anything on their own, and precisely why they rely on GAO. If an agency can decline an audit because the person who asked lacks a gavel, then oversight becomes something the majority grants to itself and withholds from everyone else. It is a tidy arrangement for whoever holds the majority, and a fine reason for whoever loses it to wish they had objected sooner.

For a veteran audience, the VA portion stings most. Department officials told GAO that contractors and employees serving as DOGE liaisons received access to every system that ordinary employees could reach. They then declined to say which systems, which liaisons, or at what level. GAO also notes that evidence from another agency showed a DOGE team member with access to the Veterans Health Administration’s instance of the Electronic Official Personnel Folder, and GAO could not confirm it with VA. That is a system of employment records, not medical charts. It is still not a system one wants to learn about secondhand.

DOGE arrived promising efficiency. Its host agencies have made the question of what DOGE could reach opaque for eighteen months and counting, which, in fairness, is a kind of efficiency. GAO says it has the authority and the track record to keep asking. In the meantime the rest of us are invited to take the agencies at their word, which is precisely what an audit exists to spare us.
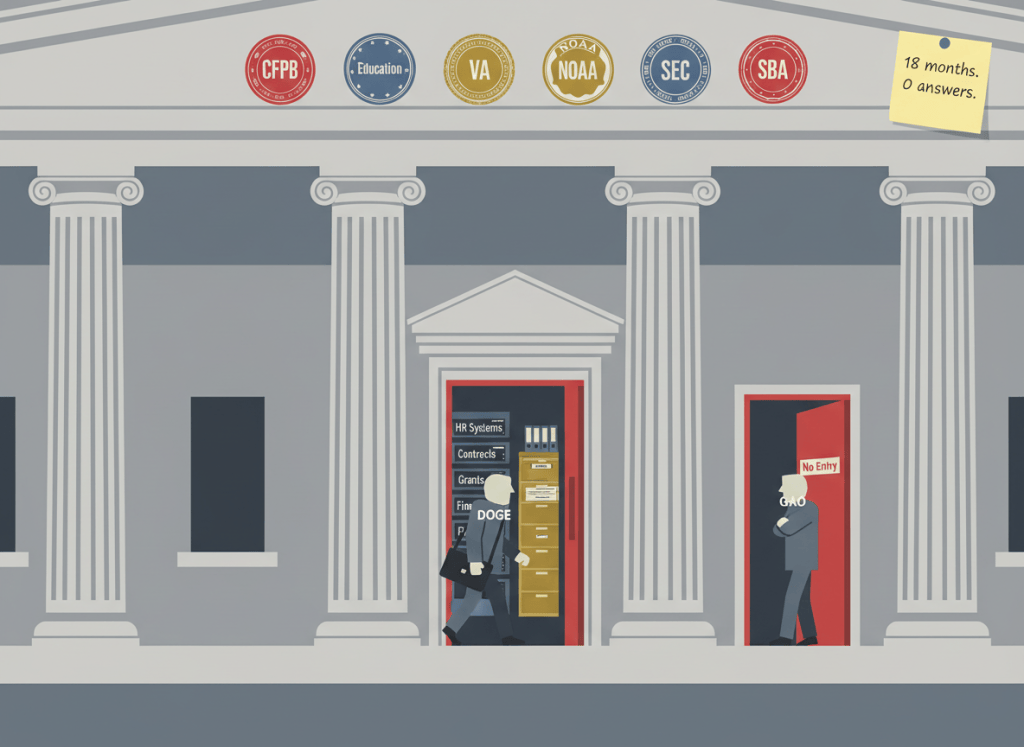
Dry editorial illustration in flat graphic style. A large government building facade — columned, institutional. The front door is wide open and a figure labeled "DOGE" walks in freely carrying a laptop bag. Beside the building, a second figure in a suit labeled "GAO" stands on the front porch, arms folded, facing a closed side door. A small sign on the side door reads "No Entry." Through the open front door, you can just make out server racks and filing cabinets labeled "HR Systems," "Contracts," "Grants," "Finances." Six agency seals line the building's facade: CFPB, Education, VA, NOAA, SEC, SBA. In the corner, a small sticky note reads: "18 months. 0 answers." Muted institutional palette: government gray, warning red, document gold, congressional blue. Flat, dry, editorial. No people faces visible.

#cybersecurity #doge #gao #congressionaloversight #dataaccess #federaloversight

0

Caricamento...

0
6

Caricamento...

The Directive That Vanished While Everyone Kept Filing the Paperwork

GAO published its third report on cybersecurity regulatory harmonization on September 28, 2026, and if y

Altro...

GAO published its third report on cybersecurity regulatory harmonization on September 28, 2026, and if you have read the first two, you already know most of what is in it. Six industry panelists from energy, financial services, and healthcare told GAO, again, that federal cybersecurity rules overlap, conflict, and cost real money to comply with. This is the fourth time since 2020 that GAO has said some version of this sentence, and the twelfth year running that information security has sat on GAO’s High Risk list. Nobody in this story is surprised by any of it, which is itself the story.

But buried in footnote 14, on page 4, is the detail that actually matters. National Security Memorandum 22, the White House directive that was supposed to be the coordinating spine of federal critical infrastructure policy, is gone. Not repealed, not superseded by a new memorandum with a different number. Just gone from the public website, “under review” since sometime before August 2026, with no explanation and no return date. GAO’s footnote is the driest possible way to report that a governing national security document disappeared from public view while the very agencies it was supposed to coordinate kept generating the conflicting paperwork it was meant to fix.

A Memorandum With No Forwarding AddressNSM-22 was signed in April 2024 to replace a decade old Obama era directive, and it did what these documents do; it named the Department of Homeland Security as the lead coordinator, designated CISA as the “National Coordinator for Security and Resilience,” reaffirmed the 16 critical infrastructure sectors, and ordered a biennial National Risk Management Plan. It was, in the language of the trade press at the time, a “good first step.” It was also, per GAO’s own report, the connective tissue between an alphabet soup of sector regulators who were each writing their own cyber incident reporting rules without much reference to each other.

That memorandum is now archived on a “frozen in time” Biden administration website, unavailable through the current White House’s own channels. GAO’s report says only that it “was under review and was no longer available on the White House’s public website” as of August 2026. There is no public indication of what replaces it, when a replacement might arrive, or whether the current administration considers the underlying coordination problem worth solving through the same mechanism. In March 2026, the White House did issue a new national cyber strategy that promised to remove burdensome or ineffective regulations and increase coordination; whatever that strategy is, it apparently did not require keeping the last coordination directive online while the new one gets sorted out.

This is the part GAO cannot say directly, because GAO audits process, not politics, but the panelists said it for them. Participants told GAO there is tension between reliability and modernization, that companies are pushed toward new technology while stuck inside compliance frameworks that do not move at the same speed. Take away the coordinating memorandum in the middle of that tension, and you have not solved the duplication problem. You have removed the one document whose entire job was to say who is supposed to solve it.

The Rule That Keeps Almost ArrivingIf NSM-22 is the memo nobody can find, CIRCIA is the rule nobody can finish. Congress passed the Cyber Incident Reporting for Critical Infrastructure Act in March 2022, giving CISA 24 months to propose a rule and 18 more to finalize it. CISA hit the first deadline, publishing its proposed rule in April 2024. It has missed every deadline since. The statutory finalization date was October 2025. CISA missed that, moved the target to May 2026, missed that too after a DHS appropriations lapse postponed a round of stakeholder town halls, held those town halls in June, and now says the rule is finally coming this month, September 2026, three and a half years after the statute that ordered it and eleven months past the deadline that statute set.

The industry panelists, naturally, have feelings about this. Most participants named the proposed CIRCIA rule or the SEC’s cybersecurity disclosure requirements as the regulations most likely to conflict with their own sector’s rules, the only two cited across all three sectors on the panel. A few in financial services walked GAO through what compliance actually looks like in practice; a single cyber incident can trigger a 72 hour reporting clock under the National Credit Union Administration, a four business day clock under the SEC, and a 24 to 72 hour clock under the still unfinished CIRCIA rule, each with its own definition of what counts as reportable. One participant put it about as plainly as a GAO transcript allows, describing what should exist instead as one report that satisfies multiple requirements where the underlying information is the same.

CIRCIA itself contains a provision meant to do exactly that, letting a covered entity skip reporting to CISA if it already reported “substantially similar” information to another agency on a similar timeline. It is a good idea sitting in a rule that has been not yet final for three and a half years, which means the harmonizing mechanism industry keeps asking for has existed on paper since 2022 and has never once taken effect.

Same Six Chairs, Same ComplaintsGAO’s methodology section is almost touching in its consistency. This is the third panel in a series that started in 2025, and GAO notes plainly that the views expressed in July 2026 “were generally similar” to the two prior sessions. Six panelists, three sectors, one afternoon of Zoom, and a report structure that has by now calcified into ritual; identify the duplicative regulations, quantify how many, note limited progress, list the same three suggestions that never quite get adopted (harmonize incident reporting, consolidate agency authority, increase collaboration).

What has changed between reports is not the complaints. It is the backdrop against which the complaints are being repeated. In 2025, industry was asking for harmonization while CIRCIA’s rule was merely late. By the second report in March 2026, it was later. By this third report, the rule is theoretically imminent, but the document that was supposed to make sure it plays well with SEC, HIPAA, NCUA, and everything else has quietly disappeared from public view. GAO can keep convening panels and counting regulations for as long as Congress asks it to. What it cannot do, and does not pretend to do, is explain why the coordinating apparatus keeps getting thinner every time the underlying problem gets documented again.

Six industry executives spent three hours in July telling GAO, on the record for the third time, that the federal government’s cybersecurity rules do not talk to each other. The federal government’s response, so far, has been to remove the memo that was supposed to make them.

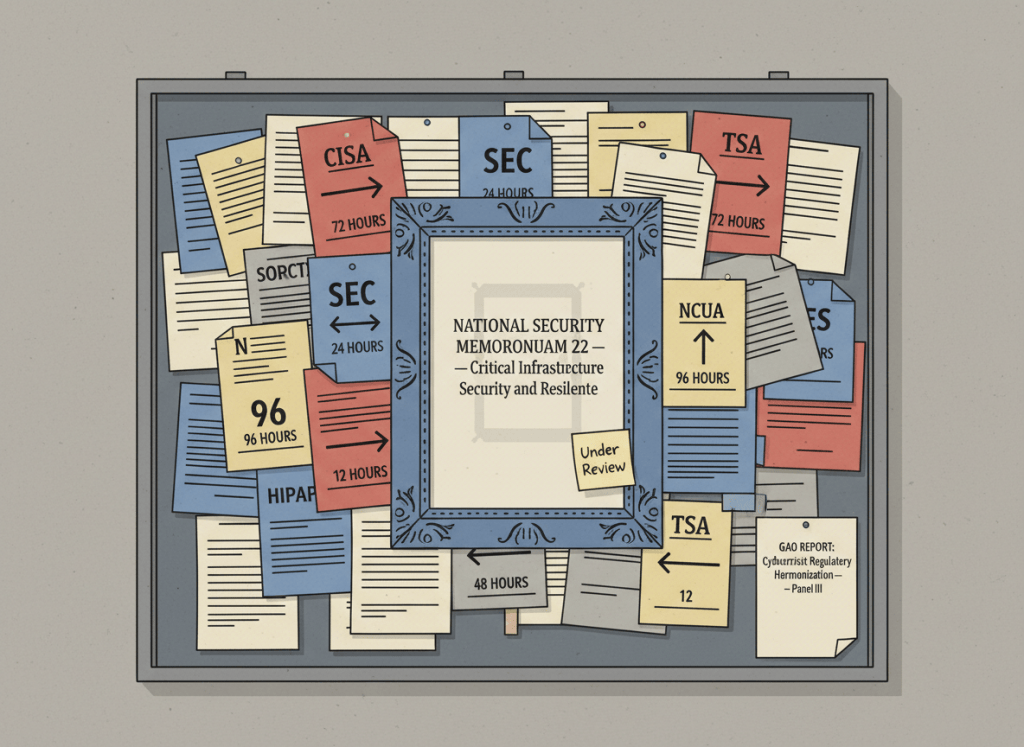
Dry editorial illustration in flat graphic style. A government bulletin board on an institutional wall. At the center, a large framed document labeled "NATIONAL SECURITY MEMORANDUM 22 — Critical Infrastructure Security and Resilience" is mounted prominently — but its glass frame is empty, just a faint rectangular ghost where the document used to be. A small sticky note on the empty frame reads: "Under Review." Surrounding the empty frame on the board: a chaotic tangle of overlapping regulatory documents from different agencies — CISA, SEC, NCUA, HIPAA, TSA — each with different reporting clocks (72 hours, 96 hours, 24 hours) and arrows pointing in conflicting directions. None of the arrows converge. At the bottom corner of the board, a single GAO report sits pinned: "Cybersecurity Regulatory Harmonization — Panel III." Muted institutional palette: government gray, federal blue, security red, manila. Flat, wry, dry. No people.

#cybersecurity #homelandsecurity #cisa #criticalinfrastructure #circia #federalcybersecurity #gao #nsm22 #regulatoryharmonization

0

Caricamento...

0
1

Caricamento...