Nearly 5,000 Danfoss-Linked Systems Found Exposed Online After Supermarket Refrigeration Attacks
Read Time:3 Minute, 42 Second
A Fresh Look at the ExposureResearchers have identified 4,980 internet-facing hosts refer
Altro...
Read Time:3 Minute, 42 Second
A Fresh Look at the ExposureResearchers have identified 4,980 internet-facing hosts refer
Altro...Read Time:3 Minute, 42 Second
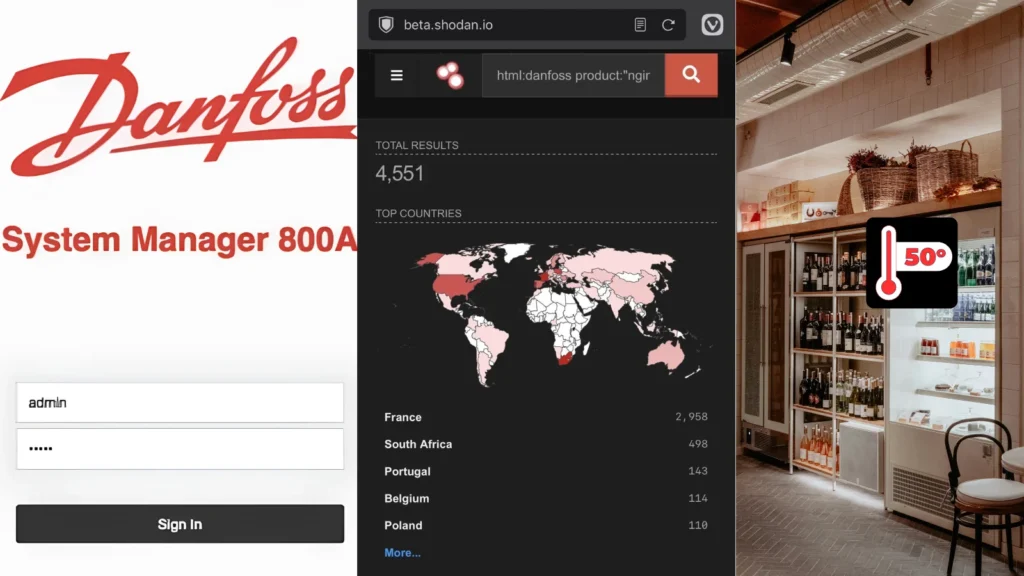
A Fresh Look at the ExposureResearchers have identified 4,980 internet-facing hosts referencing Danfoss in their web content, according to an October 13 update from the open-source intelligence account International Cyber Digest, based on a Shodan search. The finding comes just days after attackers remotely triggered defrost functions on refrigeration systems at French supermarkets overnight between October 11 and 12, spoiling chilled and frozen stock in the process. Earlier reporting indicated affected stores saw internal temperatures climb as high as 50°C during the incident.
France accounts for the largest share of exposed hosts by a wide margin, with 2,911 results, or roughly 58% of the global total. South Africa follows with 517, then Germany with 171, Portugal with 158, and the United States with 141. Smaller numbers appear in Poland, Belgium, Sweden, Spain, and the Netherlands. International Cyber Digest estimates that around eight in ten of the identified hosts are located in Europe.
What the Numbers Don’t ProveIt is worth being precise about what a Shodan search like this actually shows. The scan looks for pages that reference Danfoss in their web content, not confirmation that every listed host is a vulnerable refrigeration controller, or that any individual system has already been compromised. A separate, more filtered search returned a slightly lower figure of 4,551 results. Neither search reveals firmware versions, confirms successful attacks against specific hosts, or indicates how many individual stores each exposed controller manages.
France Confirms Widespread CompromiseFrance’s national cybersecurity agency, CERT-FR, issued an alert on October 12 confirming numerous compromises involving Danfoss AK-SM and AK-SC refrigeration management devices, and instructed operators to immediately disconnect affected systems from the internet or restrict access through other means.
Danfoss has acknowledged that the affected refrigeration management systems were running outdated firmware, and has repeated its standing advice for customers to update supported equipment and retire legacy systems that no longer receive security patches.
A Date-Based Authentication BypassIndependent research from industrial security firm Claroty’s Team82 points to a specific weakness that may help explain how attackers gained access. The team found that the AK-SM 800A platform generates a daily administrative authentication code based on the device’s current date, meaning anyone who can reproduce the underlying algorithm could calculate a valid code and obtain an administrative session, effectively bypassing the system’s configured password entirely.
That flaw is now tracked as CVE-2025-41450, affecting AK-SM 8xxA firmware versions earlier than R4.2, which Danfoss has since patched. The U.S. Cybersecurity and Infrastructure Security Agency’s advisory also lists two related flaws in versions prior to R4.3.1: CVE-2025-41451, a command injection vulnerability in the device’s email alert settings that Team82 says could allow code execution once an attacker is authenticated, and CVE-2025-41452, a web server configuration weakness that could let an authenticated attacker manipulate how web traffic is handled or disrupt the management interface.
Investigators have not publicly confirmed that this specific vulnerability chain was what enabled the French supermarket incidents. A separate, unverified claim circulating online suggests some affected systems used a default “admin” username paired with a password that simply changes to the current date, a detail that, if accurate, would make the authentication weakness especially easy to exploit without any technical skill.
Why Centralized Refrigeration Controls Are High-RiskThe AK-SM 800A is designed to manage multiple refrigeration units through a single web interface, giving operators centralized control over temperature limits, schedules, alarms, and user accounts. That convenience is also what makes exposed management interfaces so dangerous: unlike a typical IT breach, a compromise here can directly affect physical operations, in this case the cooling systems that keep food safe for consumption.
Recommended Next StepsCERT-FR’s guidance for operators who suspect compromise includes immediately restricting network access to trusted service providers, performing a factory reset, applying all available firmware updates, rotating passwords and other credentials, auditing user accounts, and fully reconfiguring the system before reconnecting it.
Remove direct internet exposure for refrigeration and building-management controllers.
Segment operational control networks away from general business networks.
Use properly secured, authenticated remote access methods rather than open internet-facing interfaces.
Verify firmware is updated past R4.2 (AK-SM) and R4.3.1 for the related flaws before reconnecting equipment.
For retailers running similar equipment, the message is clear: patching alone is not enough if the management interface remains reachable from the open internet.